The goal is a dashboard you open at http://127.0.0.1:9119 on your laptop while Hermes runs on a disposable Linux Docker host. Only an existing SSH connection crosses the public network. No domain, public dashboard port or reverse proxy is needed for this exercise.
Execution status: the recipe below has not run on a VPS. The separate recovery API test did not exercise this dashboard configuration. No dashboard, SSH tunnel, public-port result, reboot result or deployment screenshot is claimed. This is an operator-ready reference with explicit acceptance gates, not a successful-install report.
This first stage runs the dashboard only against new synthetic state. It does not start a gateway, scheduler, model-backed chat or messenger integration. Do not open a chat session, start a gateway or add scheduled work during this stage. Seeing the dashboard is not proof that an agent can complete work. Continue with the isolated restore exercise before adding real data or tools.
1. Decide the boundary before starting
Use an already-authorized, disposable Linux host, an existing non-root SSH account (UID/GID 1–65534), Docker Engine and Compose v2. Do not adapt these commands to a production Hermes directory. Allow disk space for the image and keep a way to stop the experiment. Installation, Docker-group membership, firewall changes, credential setup and reboot each deserve deliberate approval; this page does not perform them for you.
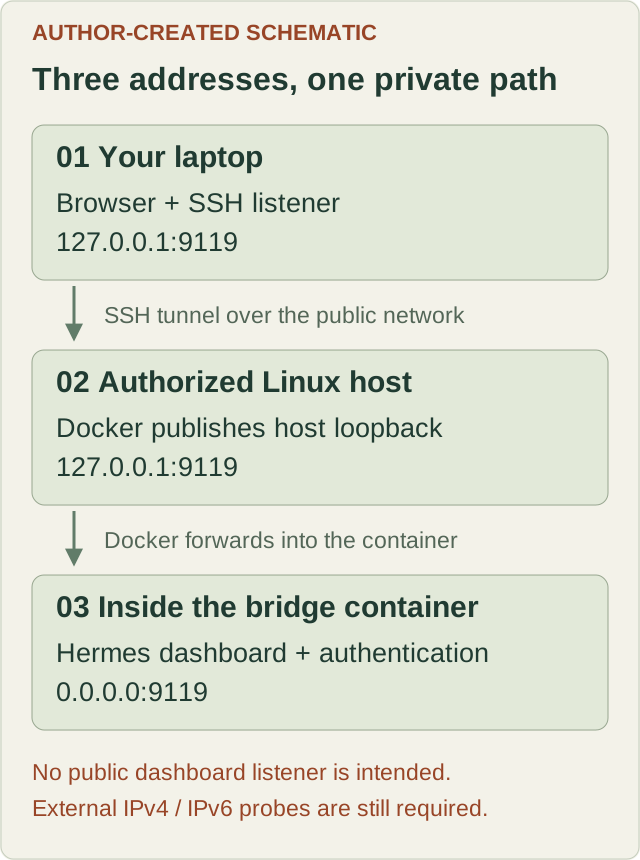
Three different addresses matter:
- Inside the bridge container, Hermes listens on
0.0.0.0:9119so Docker can forward traffic to it - On the server, Docker publishes only
127.0.0.1:9119 - On the laptop, SSH listens only on
127.0.0.1:9119and forwards to the server’s loopback address
A loopback Docker mapping does not make the application’s own bind loopback. Current Hermes requires an authentication provider for a non-loopback bind. Its old --insecure option no longer bypasses that requirement. Setting the container’s dashboard host to 127.0.0.1 instead would break ordinary bridge-port forwarding. Do not “fix” either problem by publishing 9119:9119 or disabling authentication.
A native Hermes install bound to host loopback is another design, but it is not this Docker recipe. Host networking is also a different security boundary; do not silently switch to it.
Check Docker-published ports separately from UFW. On Linux, Docker can route published-port traffic before it reaches the chains UFW normally filters, so a UFW deny rule alone does not prove a container port is private. Keep this dashboard mapped only to host loopback, leave unnecessary ports unpublished, inspect the actual Docker bindings, and test the intended boundary from another authorized machine. Disabling Docker’s firewall management is not a general fix and can break networking. See Docker’s firewall guidance.
Version gate for localhost publishing: Docker documents that releases older than 28.0.0 can expose localhost-published ports to hosts on the same Layer 2 network. Review the server Engine version recorded by docker version, not only the client version. Choose a maintained release and independently test relevant private/L2 paths as well as public IPv4/IPv6. A newer version alone is not an isolation test. These checks remain not tested here. See Docker port publishing.
2. Create new state and record the exact image
Run on the authorized server. The non-existing-directory check prevents accidental reuse of a real profile. Keep all later server commands in this shell and directory.
set -eu
umask 077
export LAB="$HOME/deploymanual-private-dashboard"
test ! -e "$LAB"
mkdir -p "$LAB/state" "$LAB/evidence"
cd "$LAB"
docker version > evidence/docker-version.txt
docker compose version > evidence/compose-version.txt
uname -sm > evidence/host.txt
cat /etc/os-release >> evidence/host.txt
docker pull nousresearch/hermes-agent:stable
export HERMES_IMAGE="$(docker image inspect nousresearch/hermes-agent:stable --format '{{index .RepoDigests 0}}')"
case "$HERMES_IMAGE" in
  nousresearch/hermes-agent@sha256:*) ;;
  *) echo 'Unexpected image identity; stop' >&2; exit 1 ;;
esac
printf '%s\n' "$HERMES_IMAGE" > evidence/image-digest.txt
export HERMES_UID="$(id -u)" HERMES_GID="$(id -g)"
test "$HERMES_UID" -ge 1 && test "$HERMES_UID" -le 65534
test "$HERMES_GID" -ge 1 && test "$HERMES_GID" -le 65534
docker run --rm "$HERMES_IMAGE" --version > evidence/hermes-version.txt
docker run --rm "$HERMES_IMAGE" dashboard --help > evidence/dashboard-help.txt
Check the selected release’s help before continuing. stable is a discovery channel; the resolved digest is the actual pin. Record it rather than inserting a guessed digest into a tutorial. Image pulls consume disk and transfer allowance even though this stage makes no model API request.
3. Configure authentication privately, then launch
The operator must first approve and complete dashboard authentication setup. Do not paste passwords, password hashes or signing secrets into chat, a command argument, screenshots or Git. Use the selected release’s interactive dashboard setup in a private terminal, with recording off:
docker run -it --rm \
  -e HERMES_UID -e HERMES_GID \
  --mount "type=bind,src=$LAB/state,dst=/opt/data" \
  "$HERMES_IMAGE" dashboard --host 0.0.0.0 --port 9119 --no-open
This setup container publishes no host ports. The restrictive umask above protects new lab directories; keep the saved authentication configuration private. Current upstream offers interactive username/password setup when no provider exists; complete that prompt yourself, then stop this temporary process with Ctrl+C. If your pinned release lacks the prompt, stop and consult its authentication documentation, rather than putting a plaintext password in the sample. Confirm the provider configuration persists under the new state directory. The current interactive flow persists a signing secret with the password hash, so that configuration should retain sessions across restart; a separately configured provider with no stable secret may use process-local signing and require a fresh login. The dashboard credential is not a model-provider key.
Save this as compose.yaml in $LAB. It starts only the dashboard, not gateway run:
services:
  dashboard:
    image: ${HERMES_IMAGE:?Set the recorded image digest}
    command: ["dashboard", "--host", "0.0.0.0", "--port", "9119", "--no-open"]
    restart: unless-stopped
    environment:
      HERMES_UID: ${HERMES_UID:?Set the operator UID}
      HERMES_GID: ${HERMES_GID:?Set the operator GID}
    volumes:
      - ./state:/opt/data
    ports:
      - "127.0.0.1:9119:9119"
    logging:
      driver: json-file
      options:
        max-size: "10m"
        max-file: "3"
docker compose -p deploymanual-private config --quiet
docker compose -p deploymanual-private up -d
docker compose -p deploymanual-private ps
CID="$(docker compose -p deploymanual-private ps -q dashboard)"
test -n "$CID"
docker inspect --format '{{json .HostConfig.PortBindings}}' "$CID" \
> evidence/port-bindings.json
ss -ltn > evidence/listeners.txt
curl --noproxy '*' --fail --silent --show-error \
--retry 10 --retry-connrefused --retry-delay 2 --retry-max-time 45 \
--connect-timeout 2 --max-time 5 \
http://127.0.0.1:9119/api/status > evidence/dashboard-status.jsonThe HTTP commands retry startup connection refusals with a bounded wait; persistent failure stops the check. Expected acceptance criteria, not observed output: one running dashboard service; port binding 127.0.0.1:9119; status indicates auth_required: true and the configured provider. Inspect startup logs locally if necessary, but redact secrets before saving or sharing them. A running container with a failed dashboard is a failure. ss alone may miss Docker NAT publishing: inspect the Docker mapping as well.
4. Open the tunnel from your laptop
Use your already-verified SSH host alias. Do not disable SSH host-key checking. Confirm the local port is free, then keep this command in a dedicated terminal:
ssh -a -N -T \
  -o ExitOnForwardFailure=yes \
  -o ServerAliveInterval=30 -o ServerAliveCountMax=3 \
  -L 127.0.0.1:9119:127.0.0.1:9119 YOUR_EXISTING_SSH_ALIAS
Replace YOUR_EXISTING_SSH_ALIAS with the authorized host alias. Open http://127.0.0.1:9119 in your laptop browser. Sign in privately and verify the dashboard displays the intended empty lab profile. Confirm an incognito session cannot read protected session data before login. /api/status can be a public status route, so its success is not proof that protected routes are exposed.
ExitOnForwardFailure detects failure to create the forwarding listener; it does not prove the remote dashboard is healthy. If port 9119 is occupied locally, close the conflicting application or deliberately choose a different local forwarding port and record that change. Avoid ad-hoc public URL/proxy changes to work around an origin rejection.
5. Prove the public path is closed
From a separate machine outside the VPS, test only your authorized host with the tunnel closed. Use the real public IPv4 and, if assigned, public IPv6:
curl --noproxy '*' -4 --connect-timeout 5 --max-time 8 \
  -o /dev/null -w 'HTTP %{http_code}\n' http://YOUR_SERVER_IPV4:9119/
curl --noproxy '*' -6 --connect-timeout 5 --max-time 8 \
  -o /dev/null -w 'HTTP %{http_code}\n' 'http://[YOUR_SERVER_IPV6]:9119/'
Run these separately and record timestamp, exit code and result. Connection refusal or timeout is the intended result, not a successful HTTP response. Any HTTP response, including a login page or 401, means the port is reachable and this privacy gate fails. Stop the lab dashboard before investigating. Do not change firewall rules to make a failed exposure test appear successful.
A timeout by itself is inconclusive: confirm the same host is alive through the approved SSH path and the dashboard responds on server loopback, then inspect the Docker mapping. A test from the server itself is not an external test. If there is no assigned IPv6, mark IPv6 “not applicable”; if it exists but no external IPv6 probe is available, mark it “not tested”. Record relevant private/L2-network probes separately from the public probes. If a required path cannot be tested, leave that gate not tested; see the version gate in section 1.
6. Verify restart and actual host reboot separately
Create a harmless file in the state directory and record its hash. Do not add schedules or connect tools for this check.
printf 'deploymanual dashboard persistence marker\n' > state/reboot-marker.txt
sha256sum state/reboot-marker.txt > evidence/reboot-marker.sha256
cat /proc/sys/kernel/random/boot_id > evidence/boot-id-before.txt
docker compose -p deploymanual-private restart dashboard
sha256sum -c evidence/reboot-marker.sha256
curl --noproxy '*' --fail --silent --show-error \
  --retry 10 --retry-connrefused --retry-delay 2 --retry-max-time 45 \
  --connect-timeout 2 --max-time 5 \
  http://127.0.0.1:9119/api/status > evidence/status-after-container-restart.json
A container restart is not a host reboot. Arrange an approved reboot window and have the operator reboot the disposable server using its normal administration path. After SSH returns, do not manually run compose up before checking whether automatic recovery worked. Reopen $LAB, reload the non-secret image/UID/GID values if Compose needs them, and record:
cd "$HOME/deploymanual-private-dashboard"
cat /proc/sys/kernel/random/boot_id > evidence/boot-id-after.txt
if cmp -s evidence/boot-id-before.txt evidence/boot-id-after.txt; then
  echo 'Boot ID unchanged: host reboot not demonstrated' >&2
  exit 1
fi
docker ps --filter label=com.docker.compose.project=deploymanual-private \
  > evidence/containers-after-reboot.txt
sha256sum -c evidence/reboot-marker.sha256
curl --noproxy '*' --fail --silent --show-error \
  --retry 10 --retry-connrefused --retry-delay 2 --retry-max-time 45 \
  --connect-timeout 2 --max-time 5 \
  http://127.0.0.1:9119/api/status > evidence/status-after-host-reboot.json
Require Docker to have started automatically, the dashboard to respond with authentication still required, and the marker hash to match. Reopen the SSH tunnel, log in again if needed, and repeat the external IPv4/IPv6 checks. Record time until SSH recovery separately from time until dashboard readiness. A manually stopped unless-stopped container is expected to stay stopped; do not mistake that for a tested crash-recovery case.
Evidence and stop conditions
Keep the actual digest, versions, redacted mapping, status results, external probe outcomes, before/after boot IDs and marker hash together. Screenshots should show a real dashboard and real command results only after execution, with credentials, cookies and account data hidden. No illustrative terminal image can replace these results.
If any gate fails, retain the failure and stop adding features. To end the dashboard stage, stop the named Compose project using the recorded configuration and close the SSH tunnel. Keep the synthetic state for recovery review; do not run down -v or delete directories as an automatic cleanup step. Stopping a VPS does not necessarily stop billing.
Still required for a tested-tutorial label: a clean-host run of every step, real authentication and tunnel interaction, independent external probes, host reboot evidence, and matching English/Chinese results. Full agent execution, scheduler recovery, model cost, backup encryption and production hardening remain separate checks.